Network Threat Detection
Identify potential intrusions, probes, vulnerable hosts, and suspicious communications.
AI-assisted Network Security Monitoring
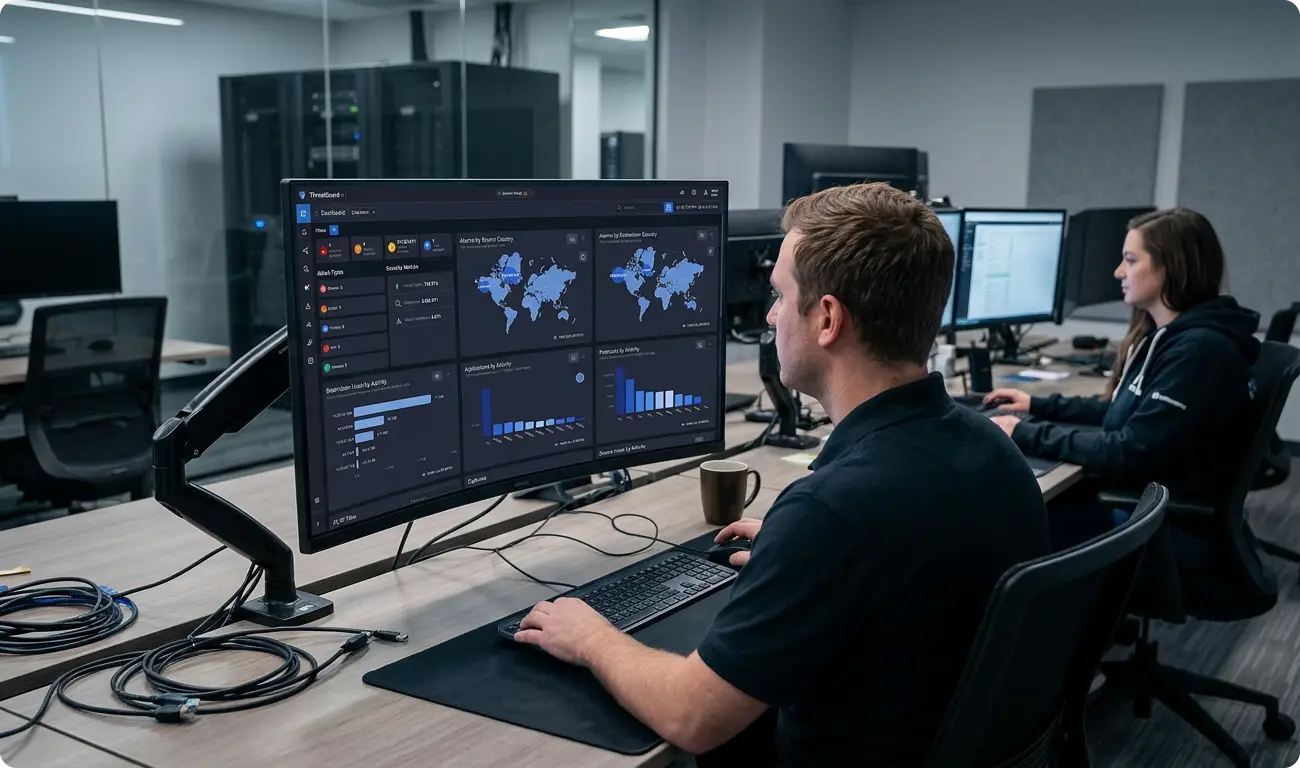
Gain deeper visibility into east-west network traffic, unmanaged devices, and suspicious activity with APCON ThreatGuard. Bring network threat detection, packet-level investigation, and AI-assisted analysis into one centralized workspace.

The challenge
Firewalls, EDR, and SIEM tools are essential, but may leave network-level investigation gaps, especially across east-west traffic and unmanaged devices.
Understand communications that endpoint-focused tools may not capture.
Reduce friction across alert consoles, analyzers, and packet captures.
Reduce friction across alert consoles, analyzers, and packet captures.
Centralize monitoring instead of assembling every workflow yourself.
The solution
From initial detection to packet-level analysis, ThreatGuard connects critical network security information in one workspace.
Identify potential intrusions, probes, vulnerable hosts, and suspicious communications.
Access alarms, hosts, sessions, and customizable dashboards.
Explore network telemetry using natural-language questions with APCON Intelligence.
Review PCAP files and packet-level evidence behind security alerts.
Visualize communication patterns and relationships between hosts.
Run as software or with APCON's integrated IntellaStore IV appliance.
Evaluate your alternatives
Open-source platforms such as Security Onion, Zeek, and Suricata provide valuable capabilities. Building a complete environment around separate tools, however, can introduce operational demands.
ThreatGuard brings detection, investigation, packet evidence, and AI-assisted analysis into a centralized experience. Compare the workflow, not just the feature list.
Investigation workflow
Connect the dots from suspicious network activity to the underlying evidence.
01
Monitor network traffic using detection rules and security alarms.
02
Examine hosts, sessions, connections, and packet captures.
03
Ask natural-language questions about network telemetry to support investigations.
Deployment
Choose the approach that fits your infrastructure and operational requirements.
Deploy on supported on-premises or cloud infrastructure.
Combine network visibility, packet capture, and security analysis.
Complement EDR, firewalls, and SIEM with network context and packet evidence.
Why APCON?
APCON brings more than 30 years of network visibility experience to ThreatGuard, connecting traffic access, packet evidence, and security analysis.
Strengthen your security investigations without unnecessarily expanding operational complexity.
See how network visibility, detection, and investigation come together in a practical security workflow.
Personalized product demonstration
Whether you're evaluating NDR software, reconsidering open-source tools, or looking to improve network threat visibility, see how ThreatGuard supports your operations.
Frequently asked questions
An AI-assisted network security monitoring platform that helps teams detect suspicious activity and investigate threats using centralized dashboards and packet evidence.
It can be evaluated as an alternative to certain open-source workflows. Suitability depends on your detection, integration, and operational requirements.
ThreatGuard complements existing investments with additional network visibility and packet-level investigation capabilities.
Yes. APCON Intelligence supports natural-language exploration of network telemetry. AI functionality requires a third-party OpenRouter API key.
As software on supported infrastructure or with APCON's IntellaStore IV appliance.
IT and security teams, SOCs, and MSSPs needing network visibility and centralized investigations.